FlyDubai Cockpit Attack: How Far Can Security Really Protect a Plane?

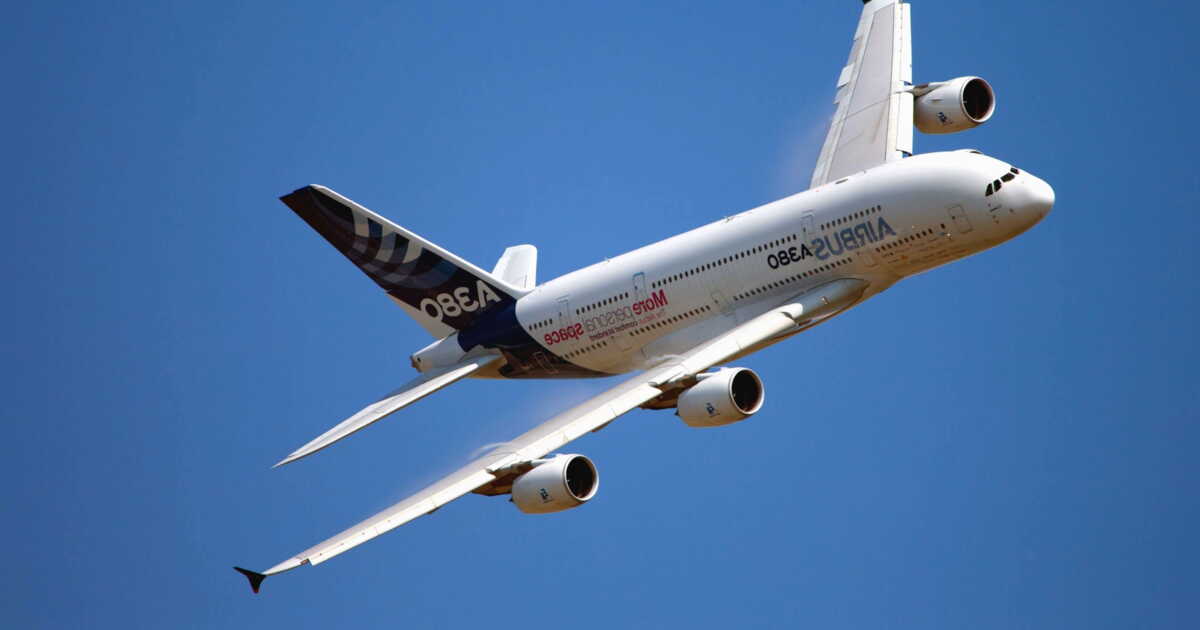
How safe are we truly when flying? The incident aboard a FlyDubai flight on September 30, 2026 has brought this question to the forefront. According to several testimonies reported after the emergency landing, the co-pilot allegedly attacked the captain with a knife, aiming to hijack or crash the aircraft, before crew members and passengers managed to force the cockpit door to subdue the assailant.

Although aviation security measures have undergone profound changes since the September 11, 2001 attacks, they were mainly designed to deter external threats. Yet, when a crew member themselves seeks to seize control of a plane, the protections are far more limited. This is explained by Jeff Price, an aviation security expert, in The Conversation.

Since September 11, 2001, the cockpit has become a true fortress

Before 2001, cockpit doors did not offer the same level of protection as today. The terrorists who hijacked four airplanes during the September 11 attacks had notably managed to gain access to cockpits and take control of the aircraft. Three planes were driven into targets, while passengers on the fourth attempted to retake the aircraft.

Since then, airlines and authorities in many countries have strengthened several layers of security. The cockpit doors have been reinforced to form a physical barrier against intrusions. Newer aircraft must also feature a second barrier designed to protect the cockpit when its door is open.

Access for crew members to secure areas has also been tightened. In the United States, for example, pilots and cabin crew undergo criminal background checks and security screenings during recruitment. They must also pass through crew-only access points and may be subjected to random physical checks.

Training has also changed. Before September 11, crews were trained primarily to comply with hijacker demands. Now, security training includes self-defense exercises and procedures designed to respond to a hijacking attempt.

In the United States, some pilots can even be armed under the Federal Flight Deck Officer program, created in 2002. To participate, they must complete training and pass weapon-handling requalifications twice a year. The Federal Aviation Administration states that these pilots are authorized to “use firearms to defend against criminal violence and air piracy when they attempt to regain control of an aircraft”.

The most difficult threat to prevent sometimes comes from within

These devices, however, have a major limitation: they are mainly designed to stop an external person from entering the cockpit. They offer far fewer safeguards when a person who is allowed to be there becomes a threat.

A particularly notable precedent occurred in 2015 with the crash of a Germanwings aircraft in the French Alps. The co-pilot prevented the captain from returning to the cockpit after leaving for a bathroom break, before deliberately causing the aircraft to be destroyed.

The FlyDubai episode thus highlights a specific safety challenge: pilots inherently have a very high level of access to the aircraft. Checks conducted before recruitment or random searches can limit some risks, but they do not prevent all actions by a determined person who is already at the controls.

Jeff Price, an aviation security expert, emphasizes this limitation of the system:

“At some point, you have to trust the individuals. It is largely on this principle that the American system rests (as it does for many other countries).”

The FlyDubai incident also draws attention to the cockpit door’s role in emergencies. According to press reports, the injured captain would have been able to unlock it, allowing passengers to enter the cockpit. This arrangement shows that protections can also be used in emergency situations when the crew needs outside help.

Thus, aviation security rests on several successive barriers, but none can completely eliminate the risk. As Jeff Price notes, even the presence of a security agent in the cockpit would not provide an absolute guarantee if that agent themselves were compromised. After more than two decades of strengthening measures against intrusions, the main challenge remains difficult to solve: securing a space without hindering the people who must work there from keeping control.
Three Cyberattacks in Three Days: Why Tourism Will Have to Prove Its Security [ABO]


Christophe Mazzola revient sur la cyberattaque qui touché 3 opérateurs du tourisme : Belambra, Maeva et Gîtes de France -  Depositphotos.com Auteur denrud

CroisiEurope


Mi-mid May, as families finalize their summer bookings and the sector enters its peak period, a single attacker reminded vacation accommodation of a truth they would rather not face. In seventy-two hours, three major players acknowledged a data breach.

On Friday, Pierre & Vacances-Center Parcs, via its platform “La France du Nord au Sud,” a subsidiary of the Maeva brand. On Saturday, Belambra and its forty-four clubs. On Sunday, the Gîtes de France network.

Three business models that were previously separated, brought together in a single weekend by the same weakness and the same method of operation.


What Was Leaked, and What No One Looks At

Each press release insisted on the same point: no banking data.
Pierre & Vacances even specifies that no e-mail address would have been collected on their side. This phrasing has become a crisis-communication reflex, and that is precisely where the misjudgment lies.

It reassures about the only risk that the general public can name, the credit card, and it distracts attention from what was actually stolen.

The loot lies elsewhere. At Gîtes de France, nearly 389,000 customers are affected, with reservations dating back to 1995, and the batch would include around 360,000 records related to minors and children registered in stay files.

Names, dates of overnight stays, e-mails, phone numbers, postal addresses. No card numbers, certainly, but enough information to craft a phishing message with perfect credibility. When the fake email cites the real date, the real place, and the child’s real first name, the victim’s vigilance weighs little.

In a sector where personal data is inherently family-oriented and spread over time, the absence of banking details is not good news; it’s a mirage.


A Sector Designed to Demonstrate

The most troubling element isn’t technical; it’s political. The hacker didn’t seek to quietly monetize their breach. They publicly claimed their action, explaining in their own words that they acted to demonstrate how porous France is in terms of cybersecurity.

In other words, these three companies did not face a sophisticated criminal operation. They served as a vehicle for a demonstration. And the choice of tourism is hardly a coincidence.

The sector accumulates the risk factors I’ve observed in the field for years. Foundations that have stacked up for three decades without anyone asking why a reservation from 1995 still exists.

A shared IT subcontracting model, where several departmental structures rely on the same provider, hence the same vulnerability. A seasonality that concentrates activity, pressure, and the lowering of vigilance on the same weeks.

And a culture where security is still seen as a technical cost line rather than as a condition of the customer relationship.


The Real Scandal Is the Data We Should Never Have Kept

What strikes me is not that these attacks were possible, but that they were predictable. The risk had been identified, sector-specific, documented for months. The missing half of the equation was the decision to act.

I call this the decision gap, the structural delta between the moment we know and the moment we decide.

A data from 1995 still exploitable in 2026 is not a technical accident. It is a retention decision that was never made, thus never arbitrated, thus renewed by default year after year. The sector has confused commercial memory with passive accumulation.

Or the data that is best protected is the one you no longer hold. Minimization and limited retention durations are not regulatory constraints to endure; they are levers to reduce the attack surface: what no longer exists in the system cannot leak.

Three decades of reservations kept “just in case” became, in a single weekend, three decades of exposed responsibility.


Digital Trust, the New Asset of Tourism


Who Is Christophe Mazzola?


Photo : Christophe Mazzola

Christophe Mazzola is a cybersecurity expert, founder of the Cyber Academy and head of the GRC practice at Cresco Cybersecurity.

His objective: to make cybersecurity accessible to everyone.

A speaker, author, and CISO, he supports companies and institutions in a pragmatic approach to digital security, at the crossroads of leadership, pedagogy, and digital sovereignty.